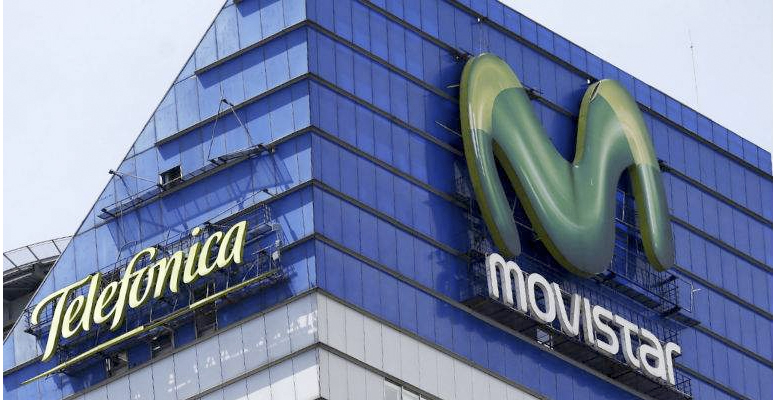
One of the world’s largest telecommunication provider, Telefonica had suffered from cyber attacks, that exposed millions of private information of its users including financial data.
The news of the breach came up when one of the user of Movistar reported the issue to a Spanish non-profit consumer rights group, FACUA. FACUA says that the user discovered that anyone with a Movistar account could view other users’ personal data. This was possible because of the improper way Telefonica designed the Movistar online customer portal.
The billing data is easily accessible by the general public simply by logging in to the system and accessing the invoice after modifying the URL. The exposed data includes critical sensitive data including mobile and landline numbers, residential
addresses, national ID numbers, names, banks, billing records and call
history, etc. The data is now available in CVS format for downloading.
FACUA has filed a complaint with the AEPD (Spanish Agency for Data Protection), which is a department responsible for implementing the newly devised GDPR rules of the EU. Under GDPR, Telefonica might be fined for up to €20m or asked to submit 2 to 4% of its annual turnover.
On this matter, Telefonica said, they have no evidence of misusing the exposed data. Moreover company have been working with the security teams and the flaw has been fixed.
Community Discussion
Join the conversation. Ask questions, share solutions, and help others.
Be the first to start the discussion!